We’re providing a summary of the board’s July 2026 meeting. The July board meeting is our only in-person meeting. The board gathers for two days of strategic thinking and long-range planning, as well as conducting annual board business. This year, we focused on allocating surplus funds we have on hand to invest in a three-year project to redesign the content system. In a related discussion, we decided to lower content registration fees starting in 2027 because we’ve had a demonstrated history of generating surpluses, exceeding what we need to run Crossref. We also discussed the board structure, as part of our regular review of stakeholder governance. And we conducted annual board business, such as approving the audited financial statements and reviewed our risk register and mitigation plans.
The resolutions are available on the dedicated section of our website, which also lists the members of the Board and offers further information about our governance.
We also managed to squeeze in watching a World Cup game over dinner.
Starting today, funder names deposited in Crossref metadata without an identifier will be matched to ROR IDs, to support an open and connected Research Nexus. Funding information is an increasingly important part of the scholarly record. The improved matching strategy supports researchers, funders, institutions, and meta-researchers, who rely on that information to understand how research is supported and what outcomes that support produces.
Strengthening Scholarly Publishing in Africa is a collaborative webinar series bringing together ASSAf, Crossref, DOAJ, EIFL, and PKP to share practical guidance, resources, and approaches for strengthening the publishing ecosystem in the region. This series responds to the growing interest in open access, digital publishing, stronger editorial practices, and greater visibility of research publishing across Africa. Each partner organisation has long experience of building that capacity in the area of their expertise. In this series, we’re coming together to offer a more holistic learning experience to the community of African publishers, putting different aspects of the publishing process in their broader context.
We’ve had a year full of growth and reached a milestone of 60+ team members; let’s take a moment to digest what that means for people operations. Hiring staff in 19+ countries is no easy task, but we are up for it, and I can honestly say it is the main reason why our culture is so great. That might sound biased coming from Crossref’s first Head of Human Resources, but hear me out.
Notification callback is a service you can use to notify you when a submission log, either in the test or production admin tool, is available for a metadata, batch query, or Cited-by query submission. Notification is provided in the form of a HTTP(S) URL where the log can be retrieved. If the notification callback service is enabled, you will no longer receive submission log emails.
The callback will be an HTTP(S) request to a URL (notify-url) provided by the member with all data relayed via HTTPS headers. The notification specifies the availability of the result, some context of the request, and an HTTP(S) URL from which to get the result. The submission log may then be retrieved using the HTTP(S) URL.
The headers use the simple name and value structure; that is, the value has no additional structure that divides it into parts. To ensure that all Unicode values can be accommodated all header values will be UTF-8 encoded.
When the notify-url is used the following HTTPS headers are provided:
CROSSREF-NOTIFY-ENDPOINT: the notify-endpoint (required) is just the name used to identify the specific notification (more on this below)
CROSSREF-EXTERNAL-ID: the id given by the member with regards to the request. For metadata deposits, for example, it is the value of the doi_batch_id element (Optional)
CROSSREF-INTERNAL-ID: the id given by us with regards to the request (Optional)
CROSSREF-RETRIEVE-URL: the URL for the member to use to retrieve the request’s result. Since the HTTPS header value is UTF-8 encoded, the URL will contain no URI encodings. For example, an Á will not be encoded as %C3%81
CROSSREF-SERVICE-DATE: the date and time stamp of the service request. Learn more about format specification in RFC 2616.
CROSSREF-RETRIEVE-URL-EXPIRATION-DATE: the timestamp after which service result is no longer available at the given retrieve-url.
Setting up an endpoint
You’ll need to set up and register an endpoint to receive callbacks.
your endpoint info (notify-endpoint and notify-url) – the notify-endpoint is just a name to identify the specific notification. The notify-endpoint should be something you can recognize so when you receive responses that include the endpoint name, it is easy to know which of the callback feeds it is coming from. Thenotify-url has to be the actual URL of your callback receiver, as that is where the notification callback transmits to via http/https
the services you’re activating the service for (metadata submissions, batch querying, Cited-by alerts)
the username and/or DOI prefix you’ll be using
if configuring the notification callback service for Cited-by alerts, you’ll need to provide us with the email address that was used to set your fl_query alerts
Make sure you inform us of any changes to your endpoint: if a message fails to send we will retry for up to a week after which you will no longer be able to receive it.
Example of a notification
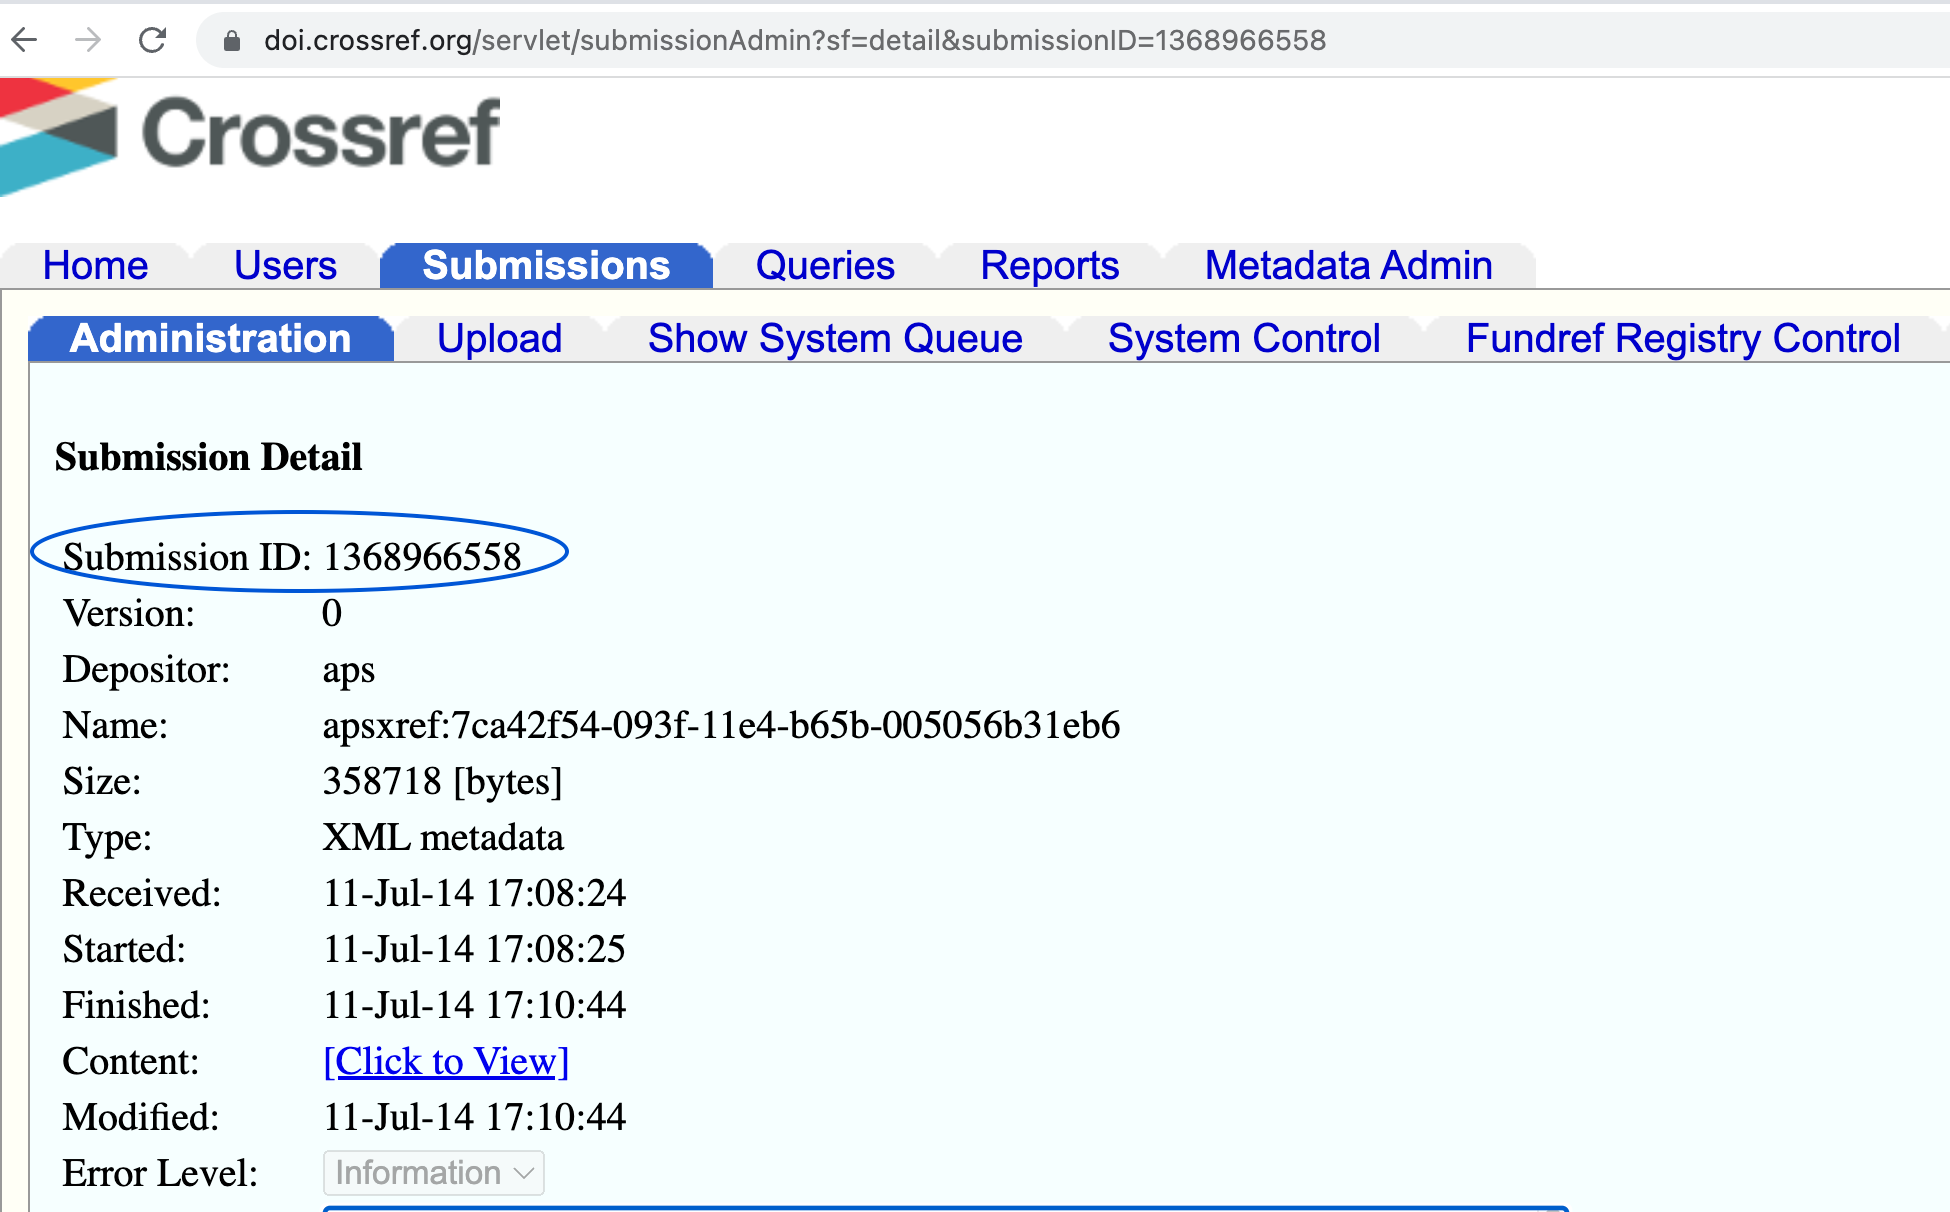
For the submission 1368966558 the notification would be as follows (new lines have been added between header name and header value to improve readability):
The notification callback service can be queried for past callbacks. The query is implemented as an HTTPS service (access control and limits to end-points and time frames TBD).
The query takes 3 criteria, the notify-endpoints, an inclusive from timestamp, and an exclusive until timestamp. All timestamps use the ISO 8061 format YYYY-MM-DD’T’hh:mm:ss’Z, for example, 2014-07-23T14:43:01Z.
The query results in a JSON array of callbacks. For example, querying for the single endpoint “1CFA094C-4876-497E-976B-6A6404652FC2” returns:
A flat structure is used to aid processing the result as a stream. There is no order defined.
The audit item is a record of attempted callbacks. It details the notify-endpoint’s notify-url used at the time of the callback, the timestamp of the callback, and the HTTPS status of the callback. If more than one attempt has been tried then the audit array will contain multiple elements; there is no order defined.
The usr and pwd are your Crossref username and password. The ENDPOINT value is a notify-endpoint or a space separated set of notify-endpoints.
A note on trusting Let’s Encrypt
We use Let’s Encrypt, a global Certificate Authority, to enable secure HTTPS connections. Please ensure your local certificate library is updated to include the letsencrypt root certificate before requesting a notification callback for your account/prefix.
Glossary of notification callback service terms
notify-url: the URL that the member provides and is used to notify them of the availability of a service request’s result. How the URL is provided to us will depend on the service.
notify-endpoint: an opaque token used to select a notify-url. The token will be anonymous and difficult to guess. The notify-endpoint is provided by the member. The notify-endpoint is associated with one notify-url (many notify-endpoints can be associated with the same notify-url).
retrieve-url: the URL that we provides that is used by the member to get the service request result.
notify-payload: the data that specifies what service request this notification is for. This payload will use HTTPS headers so as to be HTTPS method-neutral (such as POST, PUT).
retrieve-payload: the service result. Each service will define its own result content-type (that is very much like what would be sent in email today).
notification-authentication: This is the method of authentication we will use with the notify-url. Credentials are provided by the member.
retrieval-authentication: This is the method of authentication the member will use with the retrieve-url. The account credentials are provided by us.
Can the service be enabled just for our main, administrative sponsor account, and will this setting then apply to all our sponsored members?
No. We can enable the notification callback service by role and/or DOI prefix. We have to enable those roles and/or DOI prefixes one at a time.
IP addresses can change; is there a current range of IP addresses from which these callbacks will originate?
Yes. Please contact us at support@crossref.org so we can share the IP addresses that should be safelisted for this service.
Do you have a retry policy? Specifically, how many retries are attempted and at what intervals?
Yes, we do. All callbacks are created with a seven-day expiration date. They are attempted every seven to ten minutes until they receive a success, fatal failure, or they expire. Success is a http status code 200 (success) returned by the member, which then results in the callback being marked as completed.
An http status code 500 (server error) from the member is deemed as undeliverable and the callback is marked as shelved and is no longer attempted. All other responses are ignored and callbacks a retried each seven to ten minutes until the expiration is reached and the callback is marked as expired.
What is the estimated timeframe for activating the service?
Once we receive everything we need - email us the details to support@crossref.org - it takes us seven to ten business days to activate the service.
Page maintainer: Isaac Farley Last updated: 2026-June-24